
🏝️ SQLi Vulnerability Scanner Cracked
SQLi Vulnerability Scanner – SQL Injection Assessment Utility
SQLi Vulnerability Scanner is a Windows-based command-line application intended for identifying potential SQL injection issues during authorized web application security assessments. The utility processes target URLs, analyzes HTTP parameters, and records scan results through a lightweight console interface. It supports configurable threading, authentication workflows, logging, and report generation, allowing security professionals to organize and review findings as part of controlled penetration testing or internal security audits.
Tool Features:
- URL Processing – Analyze web endpoints and parameterized URLs.
- Multi-Threaded Scanning – Configure concurrent processing for assessment tasks.
- HTTP Request Analysis – Inspect web requests and application responses.
- Authentication Support – Supports authenticated scanning workflows where authorized.
- Result Logging – Record scan activity and discovered findings.
- Console-Based Interface – Lightweight command-line environment for rapid execution.
- Export Capabilities – Save scan results for documentation and review.
- Configurable Settings – Adjust scan behavior and execution parameters.
🖼️ Images
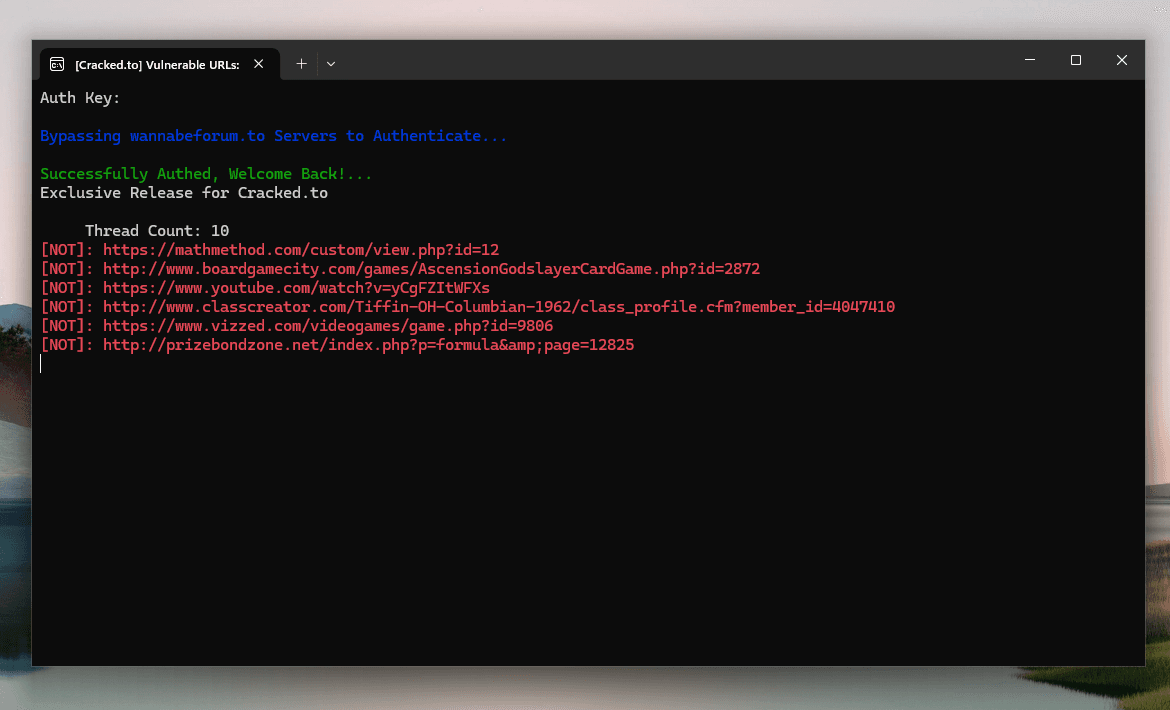
🔑 Keywords
Cracking tools are frequently detected as dangerous or malware by antivirus software, you may need to disable your antivirus or add an exception to use these tools. Use it at your own risk!
🦠 Virus Total
🔗 Links
Jul 21, 2026
Created2.088
DownloadsAds
Specials

Follow us
🏝️ More islands
10101 SOCKS4.txt
13635 SOCKS4
Bitgen Fake Transactions AIO
Bitgen Fake Transactions AIO – Ultimate Tool for Simulating Bitcoin Transactions
65K HQ Private LIVE
CRYPTO TOOLS AND BOTS | Mining, Trading Bots, Brute Checkers
Mining, Trading Bots, Brute Checkers here!
Fairy Massage - Sim
Fairy Massage – Adult Fairy Massage Simulator Game
10X NAPSTER ACCOUNTS
x208 Nord VPN Premium Accs
3947K.txt
192K GAMING USERPASS
Facebook Multi Downloader 1.0
Batch download Facebook videos in HD quality with ease using Facebook Multi Downloader 1.0
Instagram Liker
Instagram Liker – A simple tool to automate Instagram photo likes